Store › Packs › AI Governance Pack
The board asked how you govern AI. The answer is due next month.
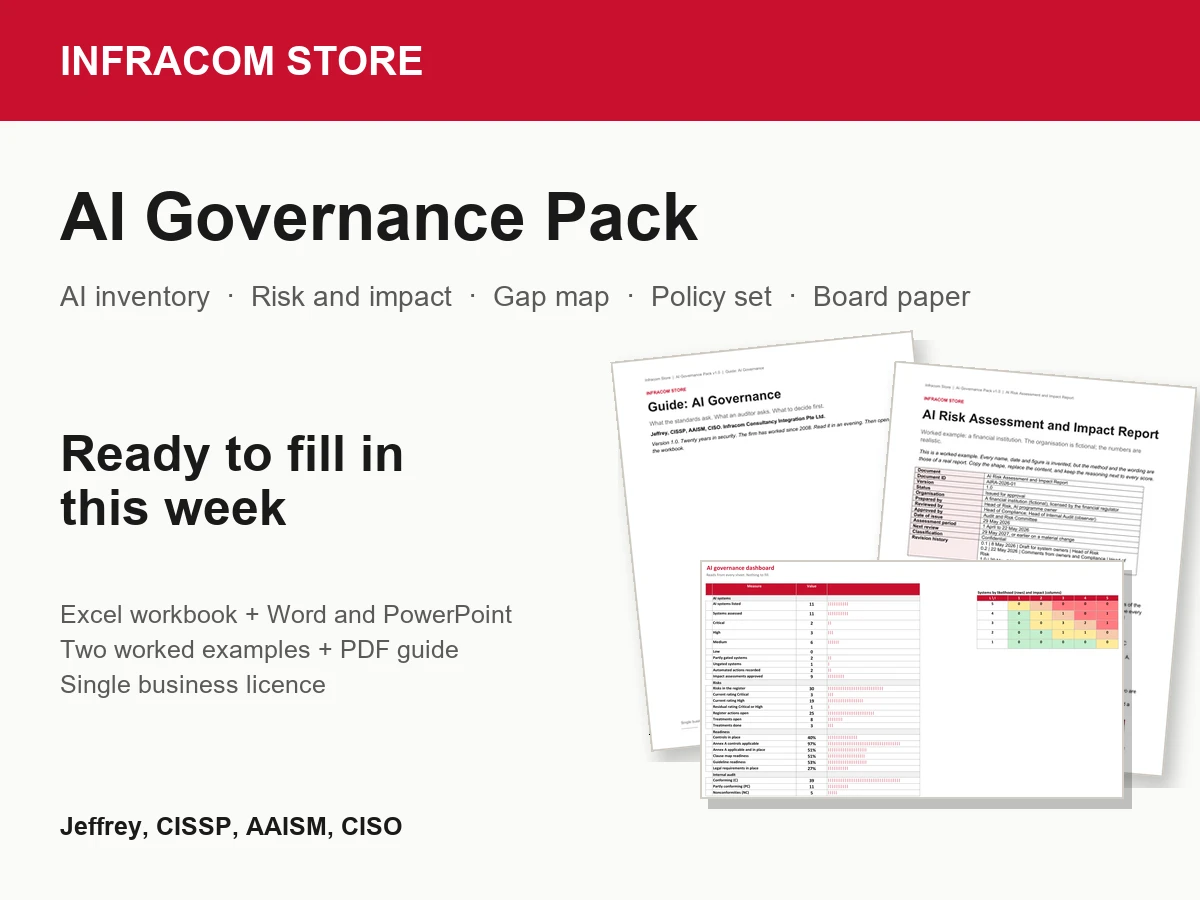
Open the workbook, list the AI systems you already run, score each one, and the heat map, the gap map and the board paper fill themselves. The policy set is ready to sign. A week of evenings, not a quarter of meetings.
Refund within 14 days if nothing downloaded · Tax invoice included · Links in your inbox within a minute
- 15 files: 2 Excel, 8 Word, 1 PowerPoint, 4 PDF
- Excel workbook, 27 sheets: AI system inventory with components and data flows, rating scales and risk matrix, assessment per system, a full-column risk register with 30 pre-written AI risk scenarios, impact assessments on eight dimensions, automated and gated actions, data sets and provider terms, legal requirements, a control library of 42 controls, threat-to-control map, the ISO/IEC 42001 statement of applicability, the 27001 to 42001 clause map, the guideline checklist, the treatment plan, a 65-question internal audit checklist, a dashboard
- Word, 8 documents: AI Policy (4,800 words, with the principles table and annexes to the 42001 themes and the NIST AI RMF functions), AI Lifecycle Procedure (seven stages with stage gates), AI Incident Procedure, Vendor Assessment Questionnaire, Impact Assessment Template, Acceptable Use Rules, Approved Tools List, Board Paper
- Two worked examples as full reports: a financial institution with 11 AI systems and a mid-size firm with six, each with the register, the impact assessments and the treatment plan, plus the filled example workbook and an internal audit report
- Instant download, free updates for life, no subscription
The walkthrough: the problem, the finished result, every file opened on screen.
Less time, fewer meetings, one picture for the board
Two weeks of e-mails asking who uses what become one afternoon. The inventory sheet asks the six questions for you.
Half the work is already done. The gap map shows what your security management system already gives you.
One page and one picture. The paper and the heat map come out of the workbook the same day you finish scoring.
The same method and wording on every client, and a worked example that shows them what done looks like.
The questionnaire answered from a dated workbook, not from memory. No consultant, no quarter lost.
You know this moment
- Staff already use AI tools. Nobody has written down which ones are allowed, or what data goes into them.
- A customer questionnaire, an auditor or the financial regulator’s AI guideline asks for an AI risk assessment you do not have.
- The board wants one page: what AI we run, what could go wrong, who owns it. You have a 300-page standard and a blank document.
- You searched for a template and found prompts, blog posts and a consultant’s day rate.
This pack is the answer to that moment. Not a course, not a standard, not a consultant's day rate: the files, filled in once, ready for you to fill in again.
Starting from a blank page, or starting from the pack
The same work either way. The difference is how long it takes and what the auditor sees at the end.
| From a blank page | With the pack | |
|---|---|---|
| AI inventory | Weeks of e-mails asking who uses what | One sheet, filled in an afternoon |
| Risk and impact per system | A blank page and a standard to read | Scored questions; the heat map updates itself |
| Gap map, ISO/IEC 27001 to 42001 | Two standards side by side, by hand | Clause by clause, already mapped |
| AI policy and acceptable-use rules | Written from scratch, reviewed three times | Adopt, put your logo on, sign |
| Board paper and management deck | The night before the meeting | Filled from the workbook |
| Outside help | A consultant: five to six figures, depending on scope | USD 149, yours to keep |
A marketplace template, a consultant, or the pack
Three ways to the same documents. What each one gives you, and what it asks of you.
| A marketplace template | A consultant | With the pack | |
|---|---|---|---|
| What you get | A document you edit by yourself | Interviews, workshops, and a tailored report | A complete workbook, policies, and worked examples |
| Who does the work | You, from a blank page | The consultant's team, over several weeks | Mostly done, you adjust and approve |
| Scoring and the gap list | Not included, you build your own | Built for you, at consultant's rates | Rating scales, risk matrix, and 30 pre-written scenarios |
| Evidence for the auditor and the board | A few filled pages, limited depth | A polished report, often without the raw working | Full register, impact assessments, audit checklist, dashboard |
| Time to a board paper | Weeks, if you have the time | Several weeks, after scoping and meetings | A day or two, slides included |
| What it costs | Under USD 100, often less | A few thousand dollars, typically | USD 149.00, once |
15 files in the pack
A 27-sheet workbook: inventory, risk register with 30 pre-written AI risk scenarios, impact assessments, control library of 42 controls, statement of applicability, the 27001 to 42001 clause map, the internal audit checklist. A policy set of eight documents, two worked examples as full reports, a 59-page guide, the deck. Filled in a week, not a quarter.
- Excel workbook, 27 sheets: AI system inventory with components and data flows, rating scales and risk matrix, assessment per system, a full-column risk register with 30 pre-written AI risk scenarios, impact assessments on eight dimensions, automated and gated actions, data sets and provider terms, legal requirements, a control library of 42 controls, threat-to-control map, the ISO/IEC 42001 statement of applicability, the 27001 to 42001 clause map, the guideline checklist, the treatment plan, a 65-question internal audit checklist, a dashboard
- Word, 8 documents: AI Policy (4,800 words, with the principles table and annexes to the 42001 themes and the NIST AI RMF functions), AI Lifecycle Procedure (seven stages with stage gates), AI Incident Procedure, Vendor Assessment Questionnaire, Impact Assessment Template, Acceptable Use Rules, Approved Tools List, Board Paper
- Two worked examples as full reports: a financial institution with 11 AI systems and a mid-size firm with six, each with the register, the impact assessments and the treatment plan, plus the filled example workbook and an internal audit report
- PDF guide, 59 pages, 21 chapters: what the standards ask, the NIST AI RMF map, what an auditor asks, the thirty scenarios, the 42 controls, buying AI, security of AI systems
- PowerPoint: management briefing, 14 slides
- How-to video inside your order page
Open it before you buy it
Real screens from the files, not a mock-up. Tap any picture to read it full size.
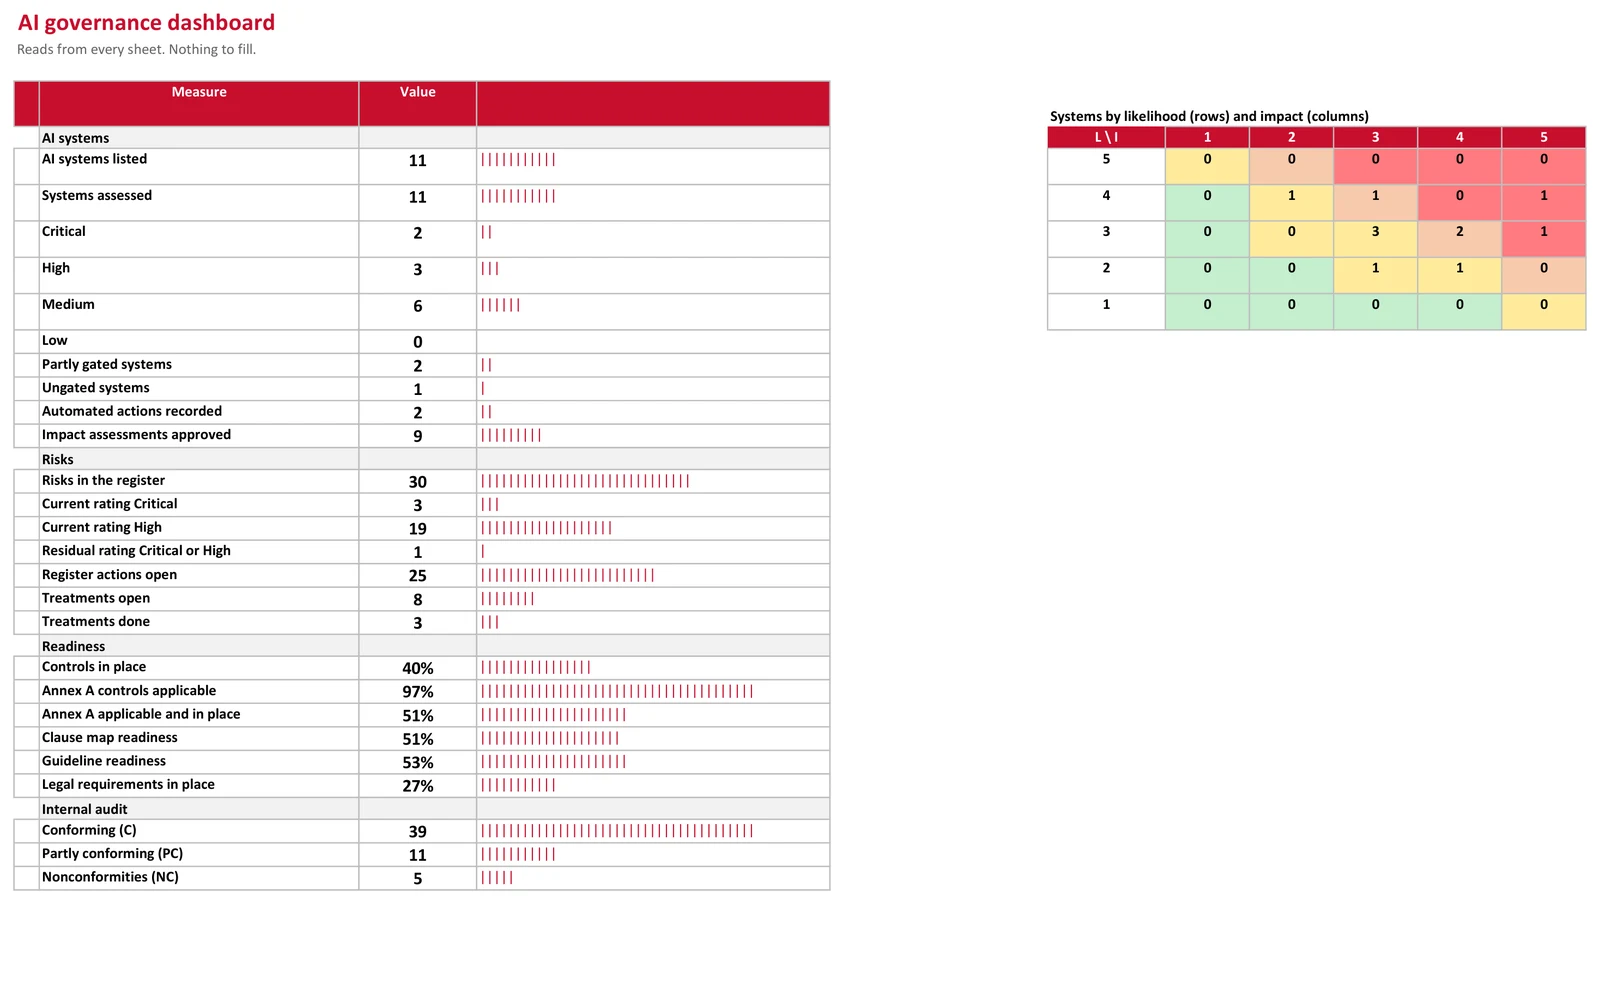
Dashboard
systems, risks, readiness and audit results, read from every sheet
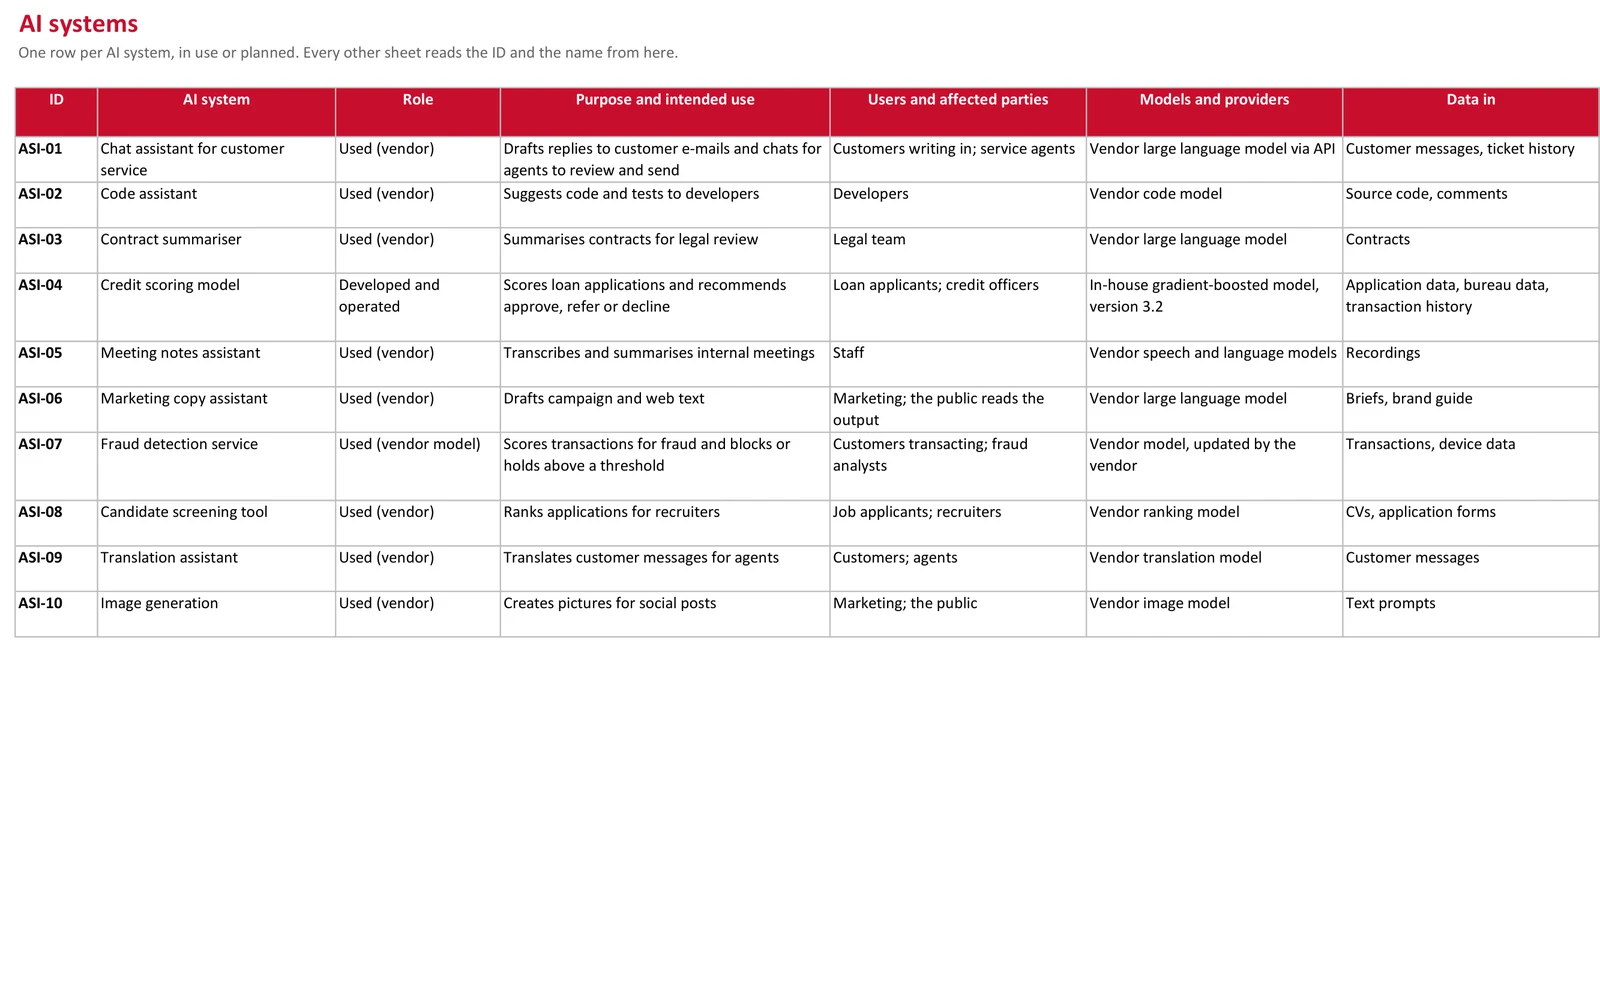
AI inventory
every system with its role, purpose, users, model, data and human oversight
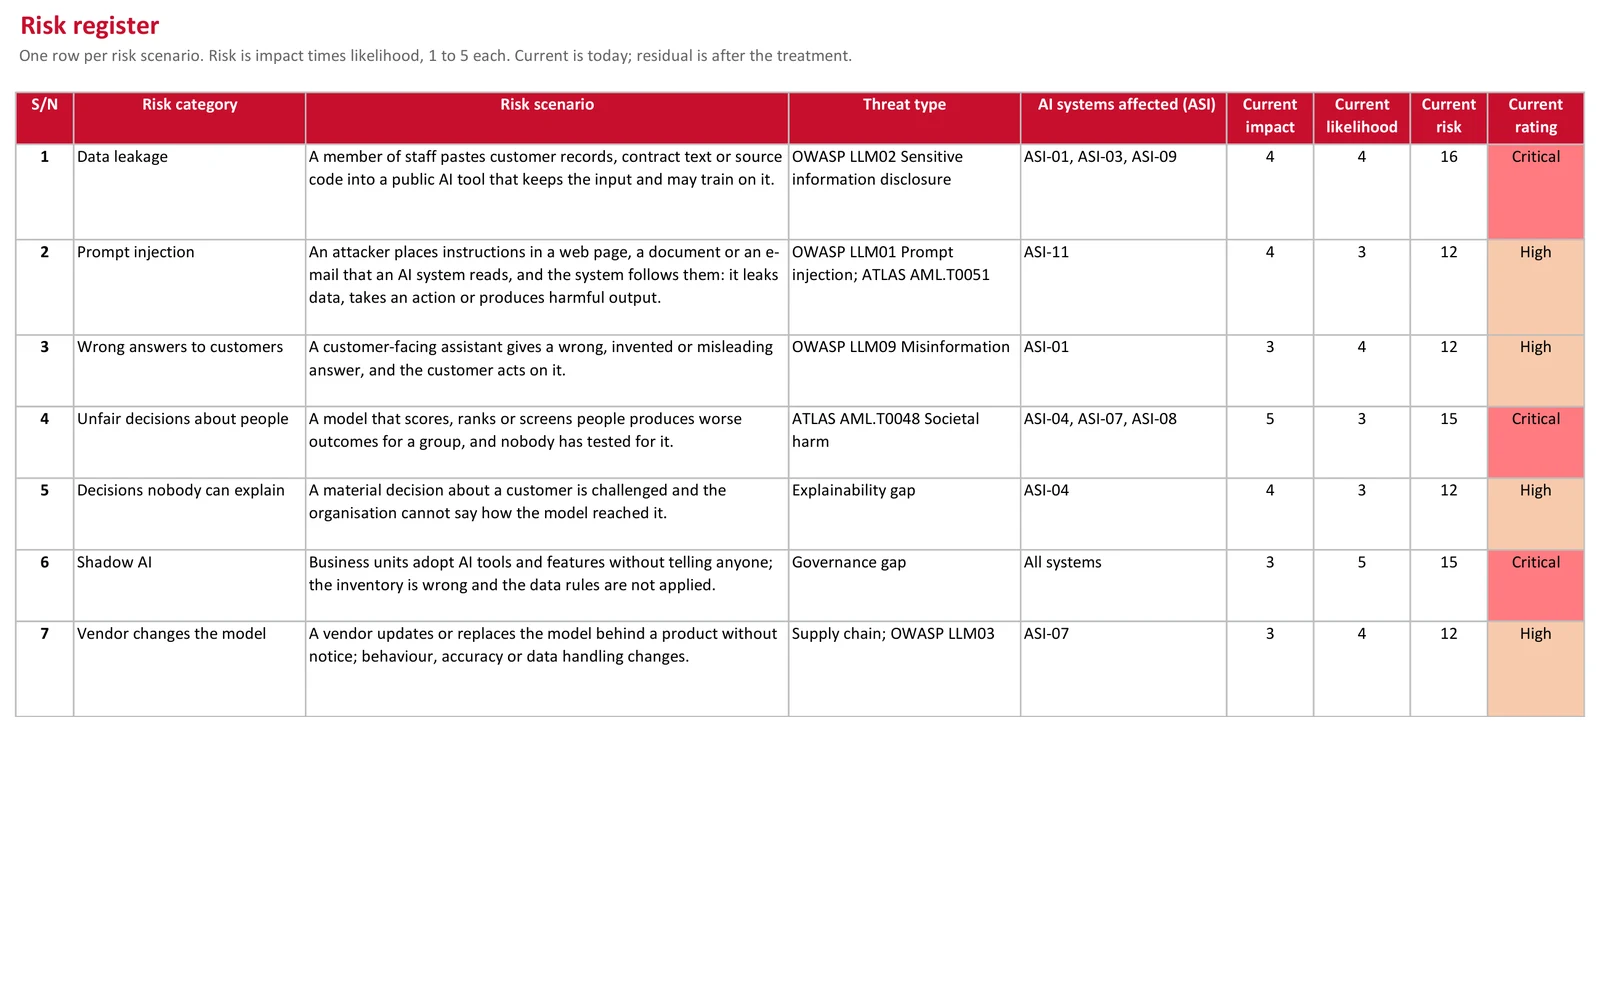
Risk register
every scenario tied to the systems it affects, scored and rated
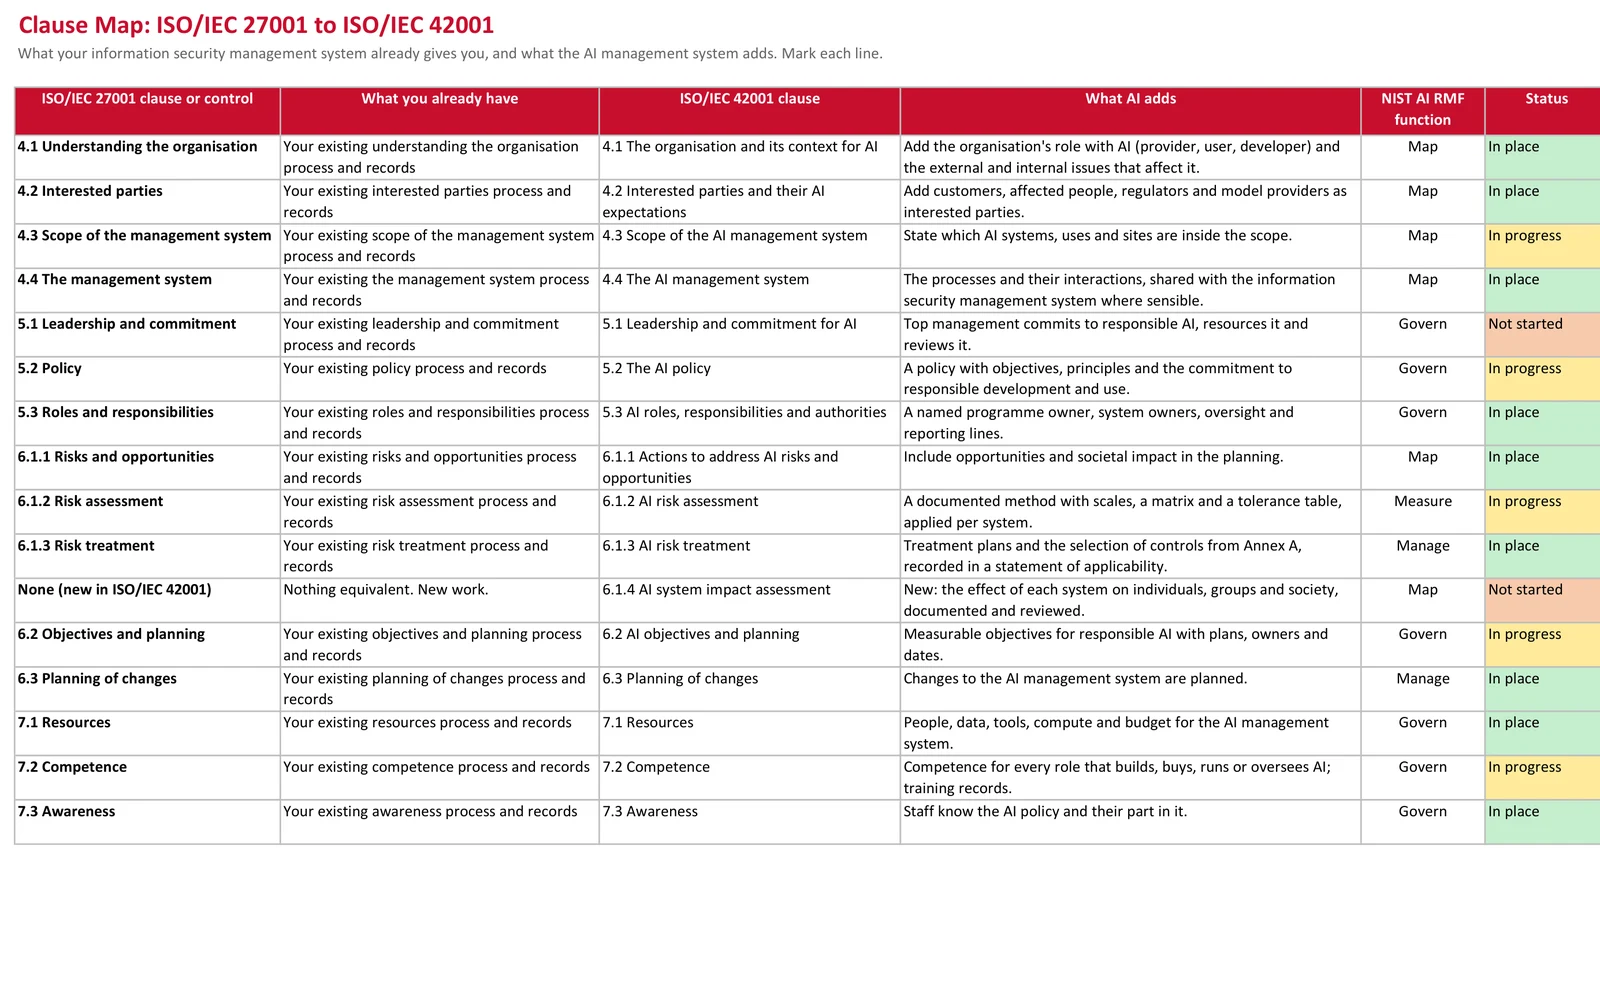
Clause map
what ISO/IEC 27001 already gives you and what ISO/IEC 42001 adds, line by line
What you can do the day you download it
- List every AI system in use, with its owner, purpose, data, components and data flows
- Start from 30 pre-written AI risk scenarios instead of a blank register, score them for your systems, and show the board one picture
- Pick controls from a library of 42, each with what good looks like and the evidence an auditor accepts
- Fill the ISO/IEC 42001 statement of applicability and see your readiness as a number
- See what your existing security management system already covers, clause by clause, and what AI adds
- Issue the AI policy, the lifecycle procedure, the incident procedure and the acceptable-use rules this week
- Assess a vendor with 20 questions before you sign, and a system with the impact assessment before you switch it on
- Run your own internal audit with the 65-question checklist, and hand the auditor a dated file
None of it starts from a blank page. Every sheet is already filled in once, in the worked example, so you copy the shape and change the facts.
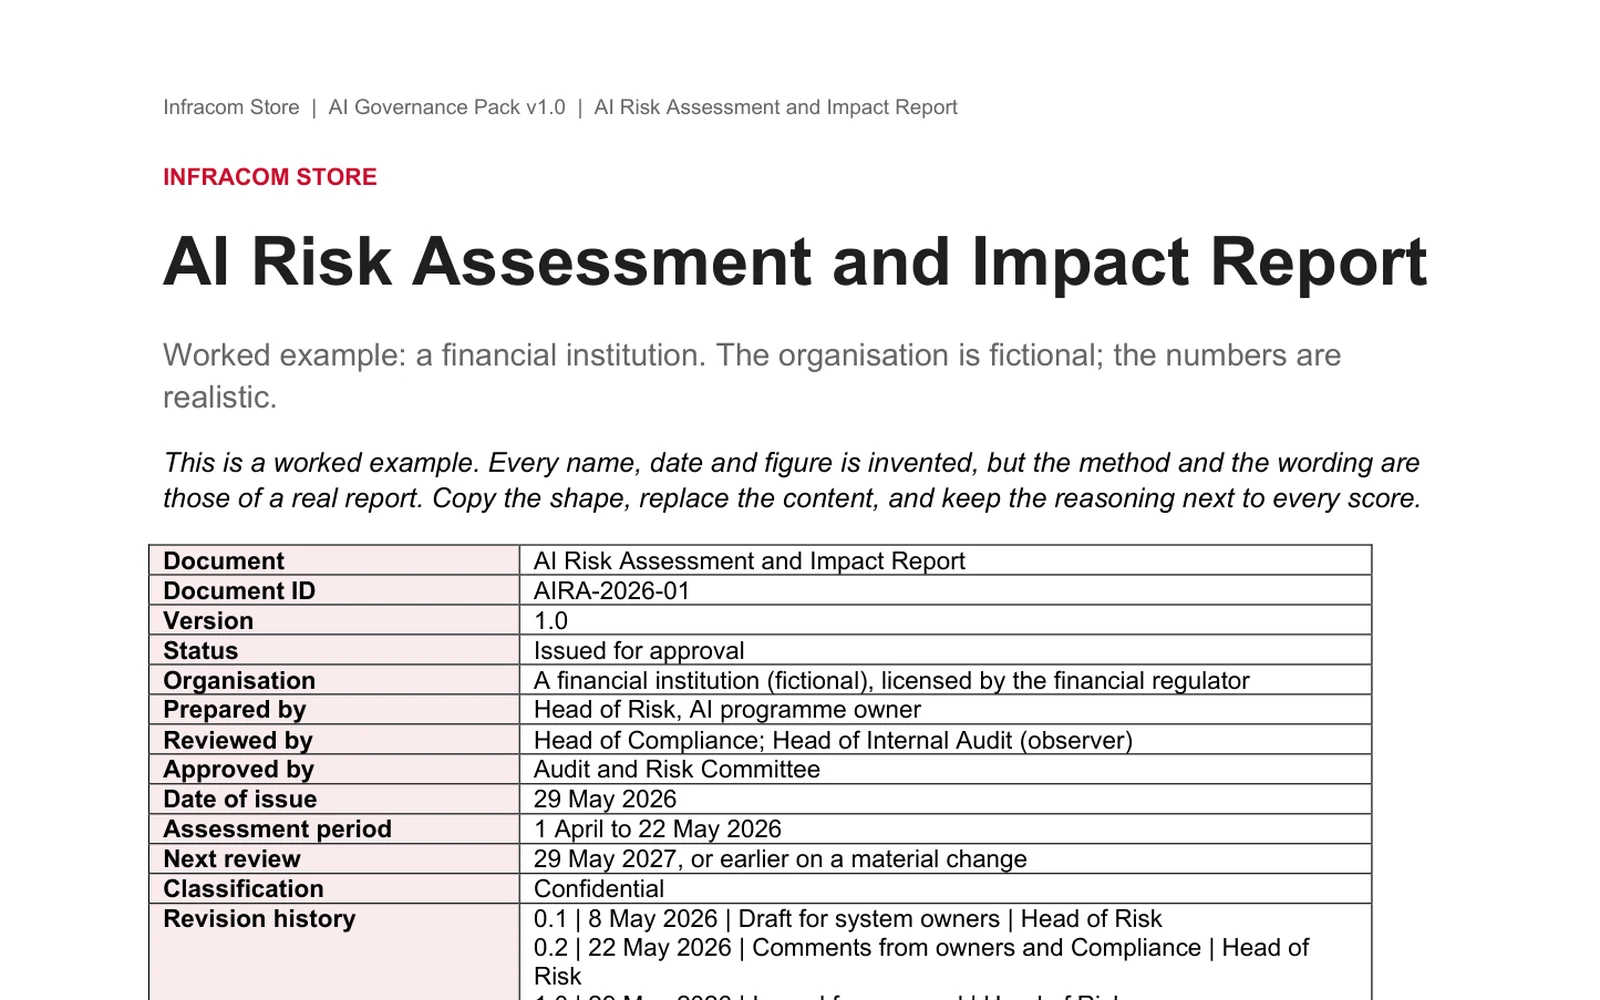
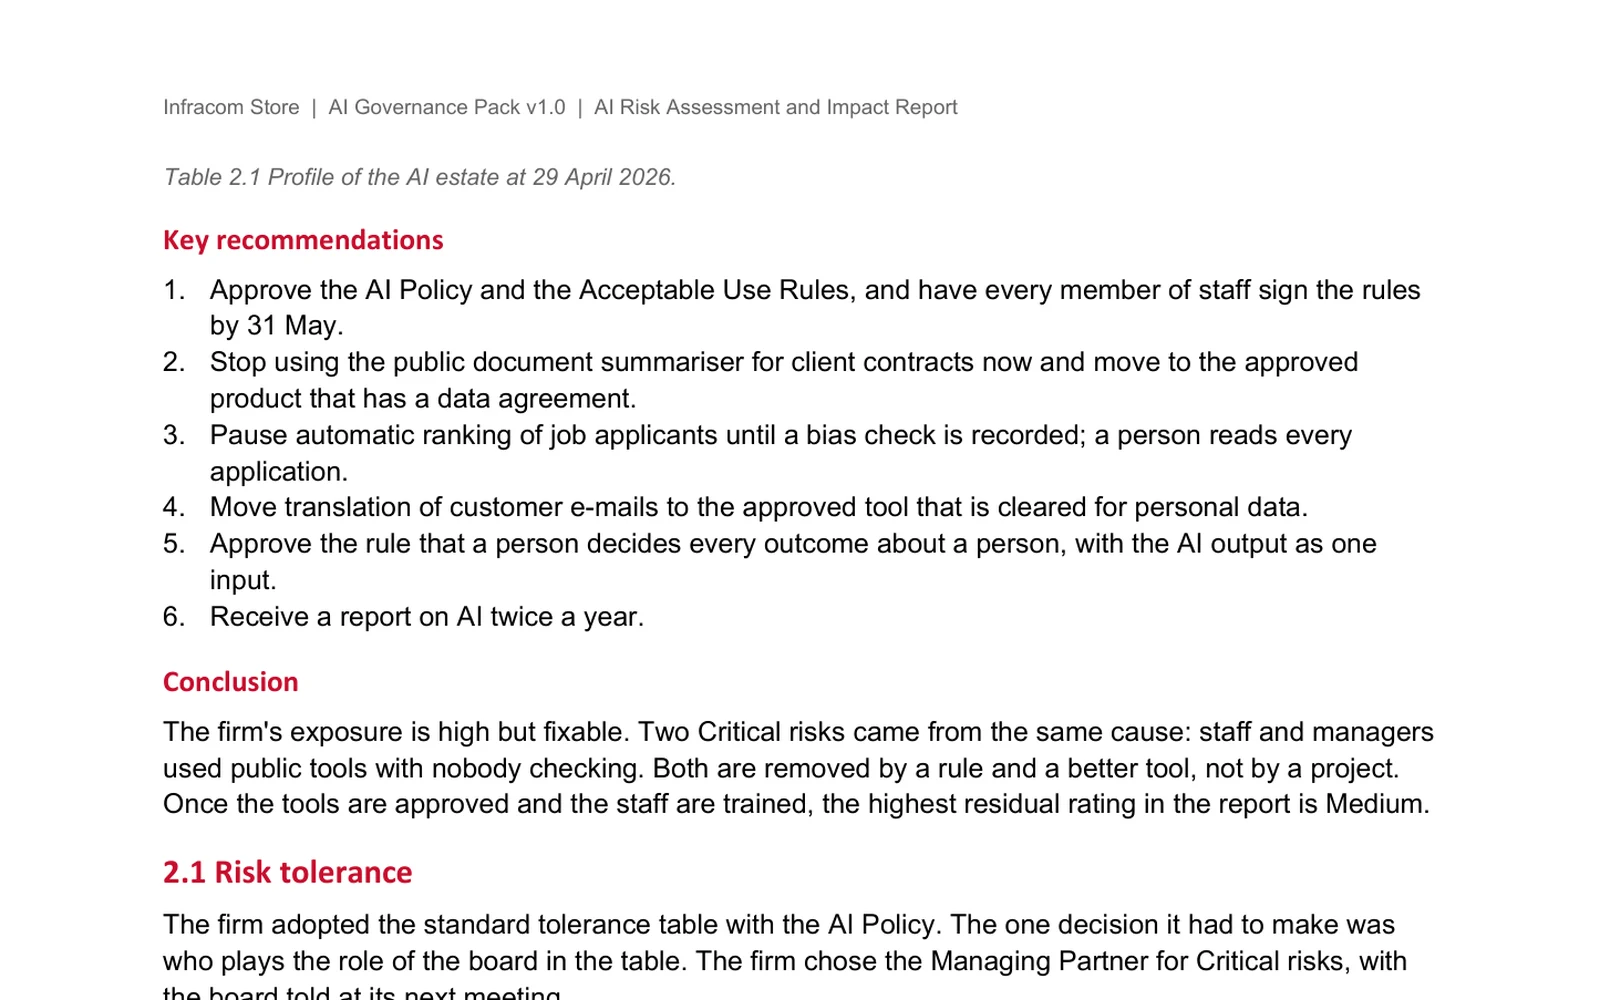
A worked example, page by page
A completed one is inside the pack, so you see where you end up before you pay.
Counted, not described
| Excel workbooks | 2 |
| Word documents | 8 |
| PowerPoint file | 1 |
| PDF files | 4 |
| Excel workbook, 27 sheets: AI system inventory with components and data flows, rating scales and risk matrix, assessment per system, a full-column risk register with 30 pre-written AI risk scenarios, impact assessments on eight dimensions, automated and gated actions, data sets and provider terms, legal requirements, a control library of 42 controls, threat-to-control map, the ISO/IEC 42001 statement of applicability, the 27001 to 42001 clause map, the guideline checklist, the treatment plan, a 65-question internal audit checklist, a dashboard | ✓ |
| Word, 8 documents: AI Policy (4,800 words, with the principles table and annexes to the 42001 themes and the NIST AI RMF functions), AI Lifecycle Procedure (seven stages with stage gates), AI Incident Procedure, Vendor Assessment Questionnaire, Impact Assessment Template, Acceptable Use Rules, Approved Tools List, Board Paper | ✓ |
| Two worked examples as full reports: a financial institution with 11 AI systems and a mid-size firm with six, each with the register, the impact assessments and the treatment plan, plus the filled example workbook and an internal audit report | ✓ |
| PDF guide, 59 pages, 21 chapters: what the standards ask, the NIST AI RMF map, what an auditor asks, the thirty scenarios, the 42 controls, buying AI, security of AI systems | ✓ |
| PowerPoint: management briefing, 14 slides | ✓ |
| How-to video inside your order page | ✓ |
| Free template | 1 |
| Updates, for life | ✓ |
From the first file to the finished programme, in order
AI Governance Pack
Open the workbook, list the AI systems you already run, score each one, and the heat map, the gap map and the board paper fill themselves. The policy set is ready to sign. A week of evenings, not a quarter of meetings.
Refund within 14 days if nothing downloaded · Tax invoice included · Links in your inbox within a minute
Stop starting from a blank page
The policy, the rules, the board paper and the deck open as finished documents. Your to-do list is the marked fields.
Every assessment is dated, scored and owned. The gap map cites the clauses. The auditor gets evidence, not a slide.
A finished assessment for a financial institution and for a mid-size firm, so you copy the shape instead of inventing it.
When the standards or the guidelines move, the workbook moves. Every update reaches you by e-mail, free, for life.
Not a template shop. A practitioner's files.
The same method and wording used on client engagements under an ISO/IEC 27001 certified organisation.
Scores, bands, treatment, residual risk. The numbers the auditor and the board both accept.
When ISO/IEC 42001 or the guidelines move, the workbook moves, and you get the update free.
Security architecture, risk, compliance and testing for enterprises, agencies and SMEs, with a licensed, CREST Pathway+ team.
Questions go to [email protected] and are answered by the team that wrote the files.
Jeffrey, CISSP, AAISM, CISO. The author line is on every file.
- Security, risk and compliance leads asked to govern AI with no extra headcount
- Boards and owners who want one page, not a project
- Firms under the financial regulator’s AI guidelines
- Consultants who want a clean, defensible starting point for every client
- You want a standard explained line by line. The guide is 60 pages, not 300.
- You want someone to run the programme for you. That is the fractional Chief AI Officer service on the main site.
- You have a date and a blank page.
- You want the files a consultant would bring, without the consultant.
A few weeks from now
Next month’s board meeting. The paper is one page: eleven AI systems, three high risks, each with an owner and a date. The policy is signed. The regulator’s checklist is answered. You built it in a week from files that were already filled in once.
That is what the pack is for. USD 149, one payment, in your inbox within a minute, refund within 14 days if nothing downloaded.
AI Governance Pack, answered
Which standards does the pack follow?
ISO/IEC 42001, ISO/IEC 23894 and ISO/IEC 42005 for the AI side, ISO/IEC 27001 for what you already have, referenced by clause. The wording and layout are Infracom’s own. No standards body endorses the pack.
We are not in financial services. Is it still for us?
Yes. The inventory, the assessment, the gap map, the policy set and the board paper are the same for any organisation. The financial-sector checklist is one extra sheet you can ignore.
Does this make us certified or compliant?
No product does. It makes you ready: a dated inventory, a scored assessment, a signed policy and a plan. Certification is an audit you then pass.
What formats are the files?
Excel for the workbooks, Word for the policy set and the procedures, PowerPoint for the deck, PDF for the guide, the worked examples and the audit report. Nothing needs a special tool.
How does this compare with a consultant?
The workbook, the policy set and the worked examples are what a consultant brings on day one of an AI governance engagement, usually ten consulting days of material. You get the files, in your format, and keep them. A consultant-led engagement costs five to six figures, depending on scope.
Can I rebrand it and use it for my clients?
Yes. The single business licence covers your own organisation and work you deliver to your own clients. Resale as a template is not allowed.
Do I get updates?
Yes, for life. Every update sends a fresh link to the e-mail address on the order.
Is there a refund?
A full refund within 14 days if nothing has been downloaded. After a download, a defective file is replaced at once.
Single business licence: your own and client work, rebrand allowed, resale not.
Digital product. Full refund within 14 days if nothing has been downloaded. A defective file is replaced at once. Terms and licence
Standards are named where the pack follows them. No standards body endorses this product, and Infracom is not linked to or endorsed by any government agency. The pack does not replace legal or regulatory advice.
Start with the free template
Gap Map 27001 to 42001: one sheet from this pack, sent to your work e-mail after one confirmation click. Then four short mails over ten days on how to use it. Unsubscribe with one click.
The board asked how you govern AI. The answer is due next month.
15 files, the worked example, one template free. One payment. Links in your inbox within a minute. Refund within 14 days if nothing downloaded.
SME Cyber Readiness Pack
Got a security questionnaire, a tender date and no plan to close the gaps?